360 Fortress
A multi-layer cyber defense system developed with a New Zealand-based company. Designed 40+ use cases spanning endpoint, network, cloud, AI and LLM security, with threat intelligence and automated response.
I turn security telemetry into useful detections, clearer investigations, and faster response.
Based in Lahore, Pakistan. I work across SIEM, endpoint and network monitoring, threat intelligence, and SOC automation — from the first alert to the final case notes.

A short, animated introduction to the areas I work in. The lines describe my portfolio; this is a visual demo, not a live security feed.
Saif Ullah is a SOC Analyst at DWP Group and a Wazuh Ambassador. His work includes Wazuh detection, n8n automation, OpenCTI enrichment, DFIR-IRIS cases and the 360 Fortress final year project.
Deployments, detection engineering, and SOC workflows across client and lab environments.
A multi-layer cyber defense system developed with a New Zealand-based company. Designed 40+ use cases spanning endpoint, network, cloud, AI and LLM security, with threat intelligence and automated response.
Integrated alerts with enrichment, case management, and Slack notifications to support triage and investigation in a practical SOC workflow.
Deployed Wazuh on AWS with BYOD onboarding, FIM, Microsoft 365 integration, multi-tenant configuration, custom branding and domain setup.
Customized a client Wazuh interface, including its login page, favicons, banners, report logos and dashboard titles.
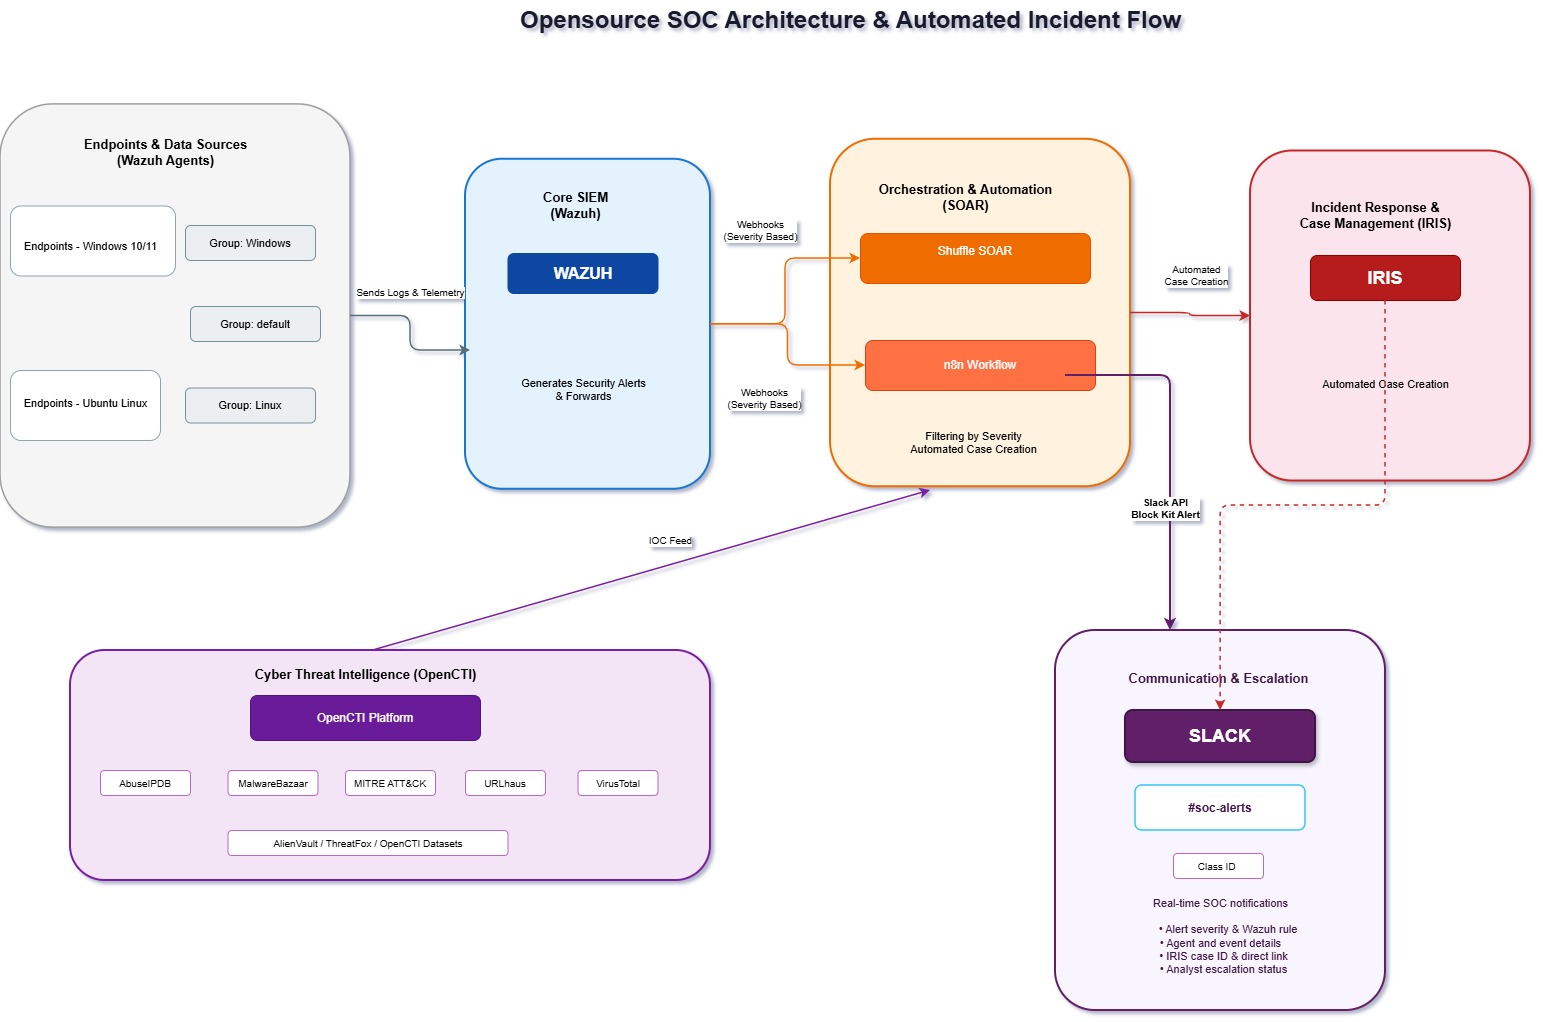
I designed and built this stack hands-on. Wazuh detects, n8n filters, OpenCTI enriches, DFIR-IRIS tracks the case and Slack tells the analyst.
Pick an alert and watch it move through the stack. Low-severity alerts stop at the filter, so no case is opened for them.
Replay totals0 alerts seen0 filtered out0 cases opened
Replay of an alert moving through the stack: an endpoint event is detected by Wazuh, filtered by severity in n8n, checked against threat intelligence in OpenCTI, opened as a case in DFIR-IRIS and announced in Slack. Low-severity alerts stop at the filter. All values shown are sample data.
Each layer is open source, so a team can adopt it without licence fees. Slack is the one exception, and it is easy to swap.
Agents on Windows 10/11 and Ubuntu Linux machines send logs and telemetry. Agent groups (Windows, Linux, default) keep each type of machine on its own configuration.
Wazuh generates the security alerts and forwards them by severity-based webhooks, so only what matters moves on.
Workflows filter alerts by severity and start automated case creation, which removes the copy-and-paste work from triage.
OpenCTI brings IOC feeds into the flow, so an IP, hash or URL is checked against known bad infrastructure before an analyst opens the alert.
Every alert that passes the filter becomes a case automatically, with the alert context attached, so investigation starts with evidence instead of a blank page.
Real-time notifications in #soc-alerts show the alert severity and Wazuh rule, the agent and event details, the IRIS case ID with a direct link, and the analyst escalation status. Mattermost or Rocket.Chat can fill the same slot for a fully open-source stack.
I built and ran this end to end. If you're weighing an open-source SOC, get in touch and we can talk through your setup.
Investigate endpoint, network and application alerts; tune Wazuh detections and dashboards; connect Wazuh, n8n, OpenCTI, DFIR-IRIS and Slack for enrichment and case tracking.
Promoted from SOC Analyst within six months. Designed multi-tenant Wazuh deployments, built detection use cases and automated alerting with security and SOAR integrations.
Triaged endpoint, network and cloud alerts with CrowdStrike, VIPRE, ELK Stack, Wazuh and Microsoft Sentinel; documented investigations and escalated findings.
Supported client security monitoring, incident documentation, Wazuh detections and practical SOC training.
Share practical content, labs and SOC use cases focused on open-source security monitoring. View official profile ↗
Wazuh, Microsoft Sentinel, ELK Stack, custom rules, FIM, log analysis
n8n, Shuffle, DFIR-IRIS, TheHive, response workflows
CrowdStrike, VIPRE, Sysmon, Suricata, Snort, pfSense, Sophos
AWS, Azure, Microsoft 365, OpenCTI, VirusTotal, AbuseIPDB
Explore my Wazuh community work, code, professional profile and verified badges.
Download my current résumé and review selected training.
My attached two-page résumé, covering SOC experience, projects, technical skills and training.
Download résumé ↓Cisco Junior Cybersecurity Analyst Career Path, Ethical Hacker and Cyber Threat Management; Microsoft Learn modules in Sentinel, KQL, Defender for Endpoint and Defender XDR.
View verified badges ↗Reach out about SOC operations, Wazuh deployments, detection use cases, or security automation.
Send an email ↗